You need a role with the Roles settings permission to create or modify roles. See Permissions reference.
System roles
Every workspace has four system roles. They show a System badge in the list. You can view them, but you can’t modify them.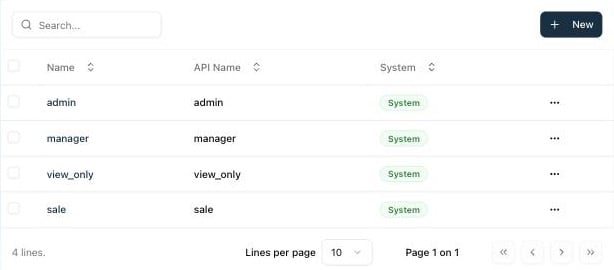
Custom roles
Create custom roles when the system roles don’t match your organisation. Custom roles show a Custom badge in the list and can be edited or deleted. Use custom roles to:- Grant partial access to some object families (for example, catalogs only)
- Restrict actions on an object family (for example, read customers but never delete them)
- Limit which quotes users can access with the Project Access Level
- Enable or disable CSV imports and exports
The permission model
A Qwoty role configures permissions in three areas: Objects, Settings, and Apps. The Permissions reference lists every permission.Objects — CRUD per object family
The Objects section controls what users can read, write, or delete, broken down by object family. You set one checkbox per action per family.Project Access Level
In the Objects section, the Project Access Level list controls which projects (quotes) a user can access:- Own: only their own projects
- Team: the projects of their teams
- Workspace: all projects in the workspace
Settings — toggle per admin area
The Settings section controls access to administration zones. Each zone has a single Authorize toggle.Settings access is all or nothing: a user either has access to a zone or doesn’t.
Apps — transversal app-level actions
The Apps section controls transversal capabilities that apply across modules.How roles work with teams
Roles define what users can do. Teams define which resources they can access. The Project Access Level in a role connects the two.Access the roles screen
1
Open Settings
In the left sidebar, click Settings.
2
Open Role
Under the Role section, click Role to view the list of roles.
View the roles list
The roles table displays:- Name: the role name
- API Name: technical identifier used for integrations and API calls
- System: a System badge for system roles, Custom for the others
Create a new role
1
Click New
Click New at the top right of the list.
2
Set the role identity
In General Information, enter the Role Name, an optional Description, and the API Name.
3
Configure object permissions
Select the Project Access Level (Own, Team, or Workspace), then check Read, Write, and Delete for each object family.
4
Configure settings access
Check Authorize for each settings zone the role should manage (Workspace, User & Teams, Roles, Data, Developers, Organization).
5
Configure app-level actions
Check Authorize for each app-level action (Import CSV, Export CSV, Overpass sales Restriction).
6
Save
Click Save. The role appears in the list with a Custom badge.
Qwoty calculates the Licence of the role automatically:
core if the role can write projects, support if it can only read projects but can write other objects. A user’s licence must match the role you assign. See Manage users.You can’t create a custom role with exactly the same permissions as
view_only.View a system role
1
Locate the role
Find the system role in the roles list.
2
Open the menu
Click the ⋯ menu to the right of the row.
3
Select View
Click View to open the role details in read-only mode.
Edit a custom role
1
Locate the role
Find the custom role in the roles list.
2
Open the menu
Click the ⋯ menu to the right of the row.
3
Select Edit
Click Edit, update the Objects, Settings, or Apps sections, then click Save.
Delete a custom role
1
Locate the role
Find the custom role in the roles list.
2
Open the menu
Click the ⋯ menu to the right of the row.
3
Select Delete
Click Delete, then confirm with Delete role.
Assign a role to a user
You assign a role when you invite a new user or edit an existing one.1
Open the user list
Click Settings, then click User in the Users & Team section.
2
Select the user
To invite a new user, click New. To edit an existing user, click the ⋯ menu on their row and select Edit.
3
Choose the role
Select the Licence, then the Role. The role list only shows roles compatible with the licence.
4
Save your changes
Click Save.
Common questions
Can I modify a system role?
Can I modify a system role?
No. System roles are locked to ensure Qwoty functions correctly. Create a custom role instead and configure the permissions to match your needs.
What happens if I delete a custom role assigned to users?
What happens if I delete a custom role assigned to users?
Reassign its users to another role before you delete it, so they keep their access.
Can a user have multiple roles?
Can a user have multiple roles?
No. Each user is assigned exactly one role. If you need a combination of permissions, create a custom role that bundles them.
What is the API name used for?
What is the API name used for?
The API name is a technical identifier used in integrations and API calls.
Do roles affect API access?
Do roles affect API access?
Yes. Each API token has a role, chosen when you create it. See API tokens.
What's the difference between Project Access Level and Read permission?
What's the difference between Project Access Level and Read permission?
Read permission decides whether a user can view projects. Project Access Level decides which ones: their own, their teams’, or all projects in the workspace.
Related
Manage users
View, invite, and edit users in your workspace.
Manage teams
Organize users into teams to control access to templates and catalogs.
Permissions reference
Every permission a role can grant.
Approvals & workflows
Set up approval rules that depend on roles and team scope.